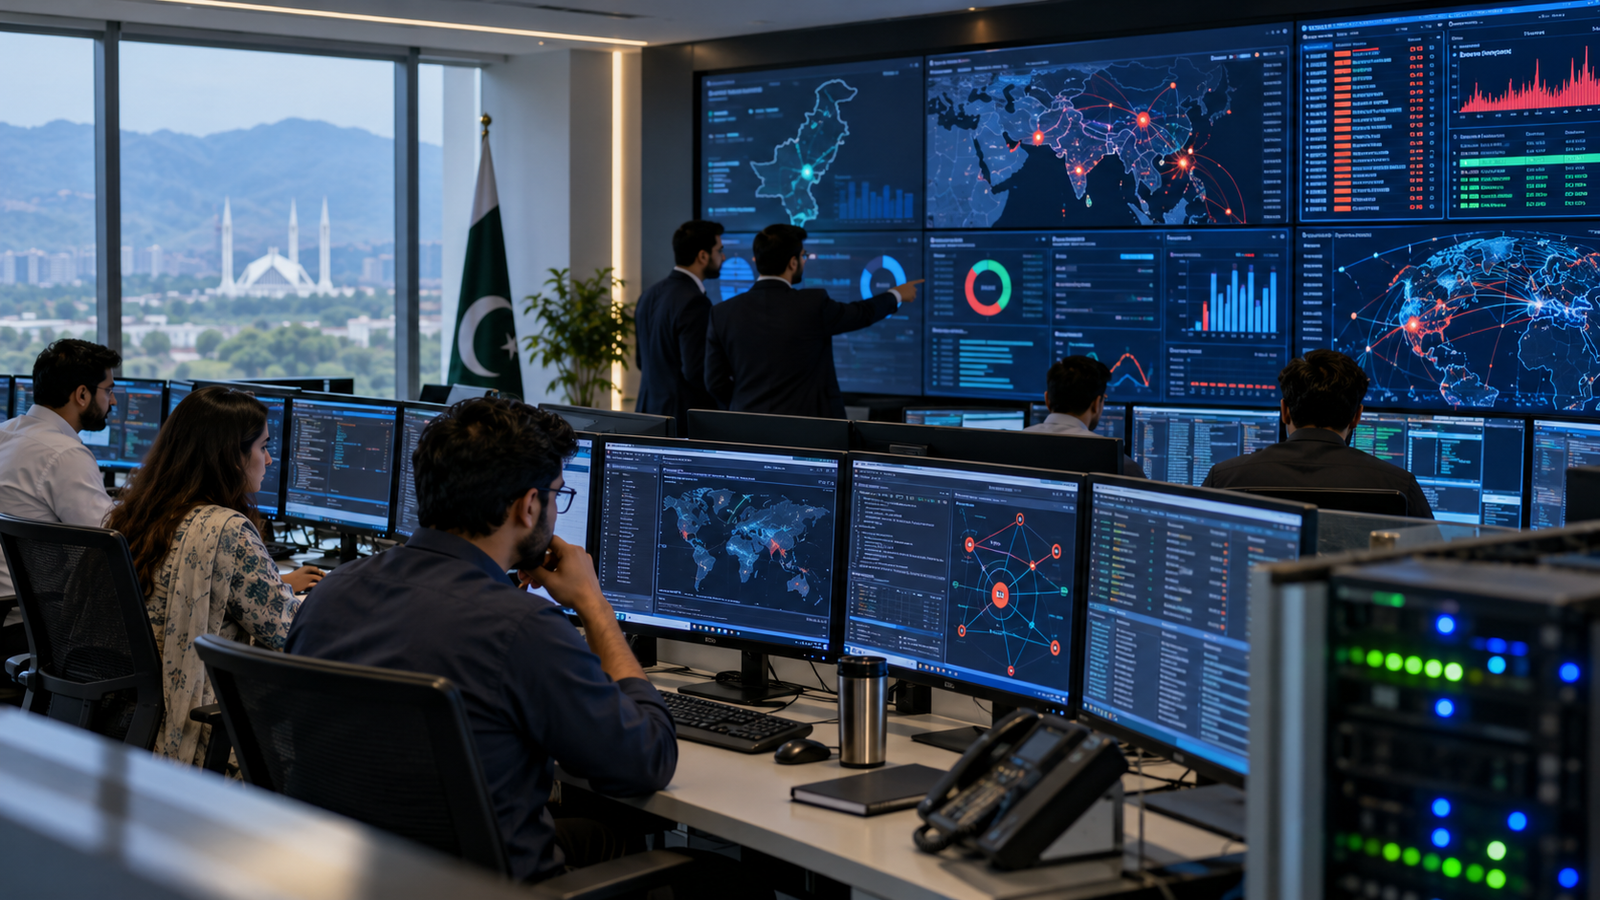
SECP Security Operations Center is now part of Pakistan’s financial regulator’s digital-defence infrastructure after the Securities and Exchange Commission of Pakistan announced its launch on October 20, 2026. The facility is intended to monitor critical IT systems, identify cyber threats earlier and enable a faster response to incidents that could affect the commission’s operations.
The official announcement, corroborated by Business Recorder, ProPakistani and Profit by Pakistan Today, says the centre provides continuous monitoring of SECP networks, servers, endpoints and private cloud environments. It also forms part of a wider plan to coordinate cyber threat intelligence and incident response among capital market institutions. Importantly, the inauguration is a confirmed event, while the broader sector-wide integration remains a plan rather than a completed nationwide network.
This Mukhbir article is published as an October 27 technology explainer about a development announced one week earlier. It is not describing the October 20 inauguration as a fresh event on October 27. The practical questions are what a security operations center does, why financial regulators need one, and what the new programme may-and may not-mean for Pakistani companies and investors.
SECP Security Operations Center: Key Facts
Organisation: Securities and Exchange Commission of Pakistan (SECP).
Facility: Security Operations Center (SOC).
Inauguration: October 20, 2026, as stated in the official press release.
Location: Islamabad, Pakistan.
Purpose: Safeguard critical information assets, detect threats early, coordinate incident response and improve operational resilience.
Monitoring scope: Networks, endpoints, servers and private cloud environments belonging to SECP.
Inaugurated by: NADRA Chairman Lieutenant General Muhammad Munir Afsar.
SECP Chairman: Dr Kabir Ahmed Sidhu.
Financing and support: Karandaaz Pakistan acting as implementing agency for the UK Foreign, Commonwealth & Development Office (FCDO); Inara Technologies Pakistan and REWTERZ supported implementation and security services.
Longer-term intention: Sector-wide threat intelligence sharing among capital market institutions and a proposed Sectoral CERT/SOC role.
Verification: SECP press releases and event gallery, plus independent reporting dated October 20.
Scope caution: There is no confirmation that every financial institution in Pakistan has already been connected to the facility.
What Exactly Has SECP Launched?
A Security Operations Center is the organisational and technical capability used to watch IT systems for suspicious activity, investigate alerts and coordinate responses. The SECP announcement describes a facility protecting the regulator’s own information infrastructure. The stated remit includes continuous visibility across endpoints such as workstations, as well as servers, networks and private cloud systems.
In the broader cybersecurity field, an SOC typically combines monitoring tools, trained personnel, documented procedures and escalation paths. A useful SOC does not depend on one screen or a collection of dashboards alone: it needs quality information, people who can interpret it and authority to act when there is a credible incident.
SECP has not published a complete technical architecture, staffing roster, detection-tool list or detailed external assessment of the facility. Those omissions are unsurprising for a security-sensitive operation, but they mean publishers should avoid confidently attributing specific software products or guaranteeing the centre’s effectiveness from the inauguration announcement alone.
Why Cybersecurity Matters for a Financial Regulator
SECP regulates important parts of Pakistan’s corporate and non-bank financial sector, including capital-market entities, insurers and other regulated businesses. Regulatory workflows depend on digital records, filings, corporate information and communications with institutions and the public. Interruptions can therefore create consequences for service delivery, market confidence and the management of sensitive data.
Cyber incidents can take many forms: credential compromise, malicious software, data theft, distributed denial-of-service attacks, disruption of suppliers or misuse of authorised systems. Financial institutions are attractive targets because they process valuable information and often rely on interconnected software systems. A regulator must consider not only its own operational continuity but also how cyber disruptions could affect the institutions it oversees.
The opening of an SOC is an organisational response to that risk environment. It should not be interpreted as proof that SECP has recently suffered a specific breach. No confirmed new attack or loss of customer records was identified in the October 20 launch statement.
Continuous Monitoring: What Will the Centre Watch?
According to SECP, the facility will continuously monitor its networks, endpoints, servers and private cloud environments. Network monitoring can help teams see anomalous traffic or communications patterns. Endpoint monitoring concerns devices through which staff interact with applications and data. Server monitoring can reveal activity affecting central services, while private cloud monitoring addresses digital infrastructure that supports internal operations.
Combining these signals may help analysts notice suspicious behaviour that a single system would miss. For example, an unusual login and an unexpected data transfer can carry different meanings when viewed independently than when correlated with other events. Analysts still need context to decide whether an alert is a technical error, authorised activity or a genuine security issue.
The centre’s ability to operate continuously is a stated capability, but its detection performance, incident-response times and coverage across every SECP system have not been independently measured in the public material reviewed.
What Is Early Threat Detection?
Early detection means finding signs of malicious activity before an incident becomes more disruptive, or at least reducing the time between an initial intrusion and a response. This can involve analysing suspicious logins, changes in system behaviour, repeated failed access attempts, malicious files or unusual outbound traffic.
An effective process generally begins with gathering reliable signals, prioritising alerts and investigating what happened. Teams then contain the problem, recover services and identify lessons that can lower the chance of recurrence. Prevention remains important, but no preventive system can guarantee that every intrusion will be blocked in advance.
SECP’s launch materials use the language of early detection and timely incident response. Those are clearly the goals of the facility. Without published performance evidence, it would be misleading to claim that the centre now prevents all cyberattacks or can identify every threat in real time.
NADRA Chairman Inaugurates the Facility
SECP’s event gallery identifies the National Database and Registration Authority chairman, Lieutenant General Muhammad Munir Afsar, as the person who inaugurated the centre. His participation highlighted the importance of cybersecurity for public institutions handling critical digital operations.
During the visit, SECP Chairman Dr Kabir Ahmed Sidhu also briefed the NADRA chairman on the commission’s IT reforms, infrastructure modernisation and interest in artificial intelligence and emerging technologies. Those initiatives were described as supporting service improvement and ease of doing business.
The inauguration and briefing are two related developments, but the public sources do not establish that NADRA will directly operate the SECP centre. Nor does the meeting mean the two organisations have merged their databases or created a publicly accessible AI service. The confirmed facts are the opening event and the stated themes of institutional cooperation and IT modernisation.
Who Supported the SECP Cybersecurity Project?
SECP said the facility was funded through Karandaaz Pakistan in its role as implementing agency for the UK government’s Foreign, Commonwealth & Development Office, or FCDO. Inara Technologies Pakistan enabled the project and REWTERZ supported it through a managed security services provider agreement.
This combination reflects how cybersecurity programmes may involve public institutions, development partners and specialist commercial vendors. Financing and technical support are not the same thing: development support may help provide resources, implementation firms may contribute infrastructure or integration, and managed security providers may assist with particular services under their contracts.
The published statement does not disclose the full project budget, procurement terms or value of individual vendor contracts. It would therefore be inappropriate to attach an invented funding amount or suggest that any one supplier owns or controls Pakistan’s financial data. Further contractual details, if publicly disclosed, would need to be analysed separately.
Will the Centre Protect Pakistan’s Entire Capital Market?
SECP plans to connect the security operations centres of capital market institutions in a shared framework for threat-intelligence exchange and coordinated response. This is a significant part of the regulator’s forward-looking strategy because security information may be useful beyond one organisation. For example, an attack pattern observed by one institution might help another improve detection.
However, the October 20 announcement describes sector-wide integration as a plan. It does not establish that all stock exchanges, brokers, depositories, clearing institutions or other market participants have already been linked or that every institution has equivalent cyber maturity.
Successful coordination would require clear participation rules, trust between institutions, data minimisation, legal safeguards and common incident-response procedures. Those arrangements can be complex when sensitive market information or personal data are involved. The practical benefit will depend on adoption and operations after the launch.
What Does Sectoral CERT Mean?
CERT commonly stands for Computer Emergency Response Team. Such teams coordinate information, advice and action in response to cybersecurity incidents. A sectoral team focuses on the risks and organisations within a particular field, such as finance or telecommunications, rather than attempting to manage every national cyber event.
SECP said the new project supports an envisioned role as a Sectoral CERT and Sectoral SOC for capital market institutions. That wording is important because the regulator described a future sectoral capability, not a fully completed designation with every operational rule already published.
A well-designed sectoral approach could support common alerts, reporting channels, exercises and information-sharing protocols. But formal powers, institutional responsibilities, reporting obligations and technical access need to be established through authorised frameworks. The launch statement alone should not be read as a new regulation requiring every Pakistani business to share data with SECP.
How Might This Affect Brokers and Market Institutions?
Banks, securities brokers, exchanges, insurers and technology service providers all face cyber risks, but their regulatory obligations differ. SECP’s announced integration specifically refers to capital market institutions and their security operations centres. It should not be stretched into an assertion that the new facility automatically supervises all financial-sector entities, including those regulated primarily by other authorities.
Potential advantages of collaboration include faster warnings about phishing campaigns, repeated attack techniques and weaknesses in commonly used software. Participants might coordinate incident notifications and lessons learned rather than responding in isolation. Yet these benefits are prospective; they are not evidence that a concrete incident was prevented during the first week after inauguration.
Companies should continue following their existing cybersecurity, data-protection and incident-reporting requirements while watching for formally issued guidance on the sector-wide framework.
What Does This Mean for Investors and Ordinary Citizens?
Investors generally need confidence that financial infrastructure can provide reliable access to records, disclosures and services. A cybersecurity incident that interrupts a regulator or related institution can create uncertainty and delay routine processes. Improving monitoring and response is therefore relevant to the resilience of the broader market ecosystem.
Ordinary citizens may benefit indirectly if digital regulatory services become more dependable, but the launch does not create a new public app, an online complaint portal or a guarantee that every private financial platform is safer. It does not change investment risk, eliminate fraud or make any particular product suitable for an investor.
Individuals should continue checking financial firms’ regulatory status, using strong account security and remaining cautious about impersonation and investment scams. A regulator’s SOC helps protect its operations but does not replace individual vigilance or business-level controls.
The Role of Artificial Intelligence in SECP’s Technology Plans
SECP Chairman Dr Kabir Ahmed Sidhu briefed the NADRA chairman on IT reform, infrastructure modernisation and the use of artificial intelligence and emerging technologies to improve public services and business processes. This signals an interest in digital transformation beyond conventional cybersecurity monitoring.
Artificial intelligence can be used in many administrative settings, including document classification, service assistance, anomaly detection and workflow management. But the public statement did not identify a particular AI model deployed in the SOC, nor did it publish accuracy or productivity measurements from a live AI system.
Editors should therefore distinguish the confirmed SOC launch from the regulator’s broader stated interest in AI. Claims such as ‘AI now prevents all market cyberattacks’ or ‘SECP launched an autonomous cyber defence system’ would go beyond the available evidence.
How This Fits Pakistan’s Wider Digital Security Efforts
Cybersecurity is increasingly relevant as Pakistan expands digital government services, corporate filings, electronic payments and online business processes. More digital activity can improve speed and convenience, but it also increases dependence on networks, software providers and safe data handling.
The SECP facility is a regulator-specific addition to that wider landscape. Pakistan’s federal authorities have separately announced national-level cybersecurity initiatives, including an August 2026 National Cyber Security Operations Centre. Those are distinct institutions and programmes. Readers should not confuse SECP’s October facility with an entirely new national SOC serving all ministries or citizens.
The regulator’s own focus is on critical SECP information assets and a proposed capital-markets collaboration framework. That narrower, clearly defined description is more useful than a generic headline implying that all cyber risk across Pakistan has been resolved.
What Are the Limits of a Security Operations Center?
An SOC can improve visibility and provide an organised way to respond, but it cannot remove every risk. Attackers may exploit previously unknown vulnerabilities, steal credentials or target suppliers. Technical systems may create false alarms, while genuine threats can go unnoticed if telemetry is incomplete or analysts are overwhelmed.
A mature cybersecurity programme also depends on secure software updates, access controls, disaster recovery, training, independent testing and governance. It must protect confidential information while retaining sufficient records to investigate incidents. Keeping response plans current and testing them can be as important as buying monitoring tools.
The strongest public assessment of SECP’s new facility will eventually come from verifiable operational progress, institutional safeguards and appropriately disclosed independent assurance. The initial ceremony alone should not be mistaken for a proven cybersecurity outcome.
Business Opportunities and Cybersecurity Skills
The project illustrates demand for specialised security services, threat analysis and digital infrastructure capabilities. Managed security providers, integration companies and cybersecurity professionals can play different roles in developing and maintaining such systems. Local businesses may see opportunities in training, secure cloud operations and incident-response support as organisations improve their defences.
Nevertheless, the SECP announcement does not promise a specific number of new jobs or grant funding to every cybersecurity startup. No recruitment timetable or public procurement opportunity should be inferred without a separate notice. The names of project partners indicate involvement in this particular programme, not official endorsement of all their commercial products.
For students and professionals, the relevant skills include network fundamentals, logging, incident investigation, secure system administration and communication. Training pathways vary, and successful cybersecurity work demands both technical competence and responsible handling of sensitive data.
What Should Mukhbir Readers Watch Next?
The next important milestone will be the proposed capital-market threat-intelligence framework. Readers should watch for official instructions on which institutions are involved, how incidents will be reported, what information can be shared and how responsibilities will be divided between firms and the regulator.
Other useful evidence would include SECP updates on operational coverage, cyber exercises, governance standards and improvements to services, where those disclosures can be made without undermining security. There may also be news about the wider digital-modernisation programme described by Dr Sidhu during the inauguration visit.
Any future claim about a prevented attack, new mandatory reporting rule or completed industry-wide integration should be assessed against a named document or official statement. As of this article’s publication date, the existing SOC launch is confirmed, but its wider sectoral programme remains an announced direction.
Conclusion
The SECP Security Operations Center is a verified cybersecurity initiative announced on October 20, 2026. Designed to monitor SECP networks, endpoints, servers and private cloud infrastructure, it aims to detect threats earlier and improve incident response. The facility was inaugurated by NADRA Chairman Lieutenant General Muhammad Munir Afsar and supported through a project involving Karandaaz Pakistan, the UK FCDO, Inara Technologies and REWTERZ.
Its potential significance extends beyond the regulator’s internal systems because SECP has outlined plans for threat sharing and coordinated cyber responses among capital market institutions. But those wider arrangements are not yet confirmed as fully operational. For investors and companies, the initiative highlights the increasing importance of digital resilience, with future progress to be judged by implementation rather than launch-day promises.
Frequently Asked Questions
What is the SECP Security Operations Center?
It is a new facility for monitoring SECP digital infrastructure, identifying potential cyber threats and coordinating timely incident response.
When did SECP launch the cybersecurity centre?
The official SECP press release is dated October 20, 2026. The event gallery identifies the October 19 inauguration coverage.
Who inaugurated the SECP SOC?
NADRA Chairman Lieutenant General Muhammad Munir Afsar inaugurated the facility in Islamabad.
What systems does the SOC monitor?
SECP says it monitors the regulator’s networks, endpoints, servers and private cloud environments.
Who financed and supported the project?
SECP named Karandaaz Pakistan and the UK FCDO funding arrangement, Inara Technologies Pakistan and REWTERZ as project partners.
Will it cover every company in Pakistan?
No. Its confirmed monitoring role concerns SECP systems; a broader capital-market institutional framework is planned, not confirmed complete.
What is a Sectoral CERT?
A Sectoral Computer Emergency Response Team coordinates cybersecurity information and incident response for a defined sector. SECP described this as an envisioned role.
Does the new centre eliminate cyberattacks?
No security system guarantees that. Its aim is to strengthen monitoring, detection, response and resilience.
About The Author